

THE JOURNAL / MUHAMMAD EISSA
Ideas for a more secure world.
Perspectives on cybersecurity, governance, and the decisions that connect them.
Latest articles 6
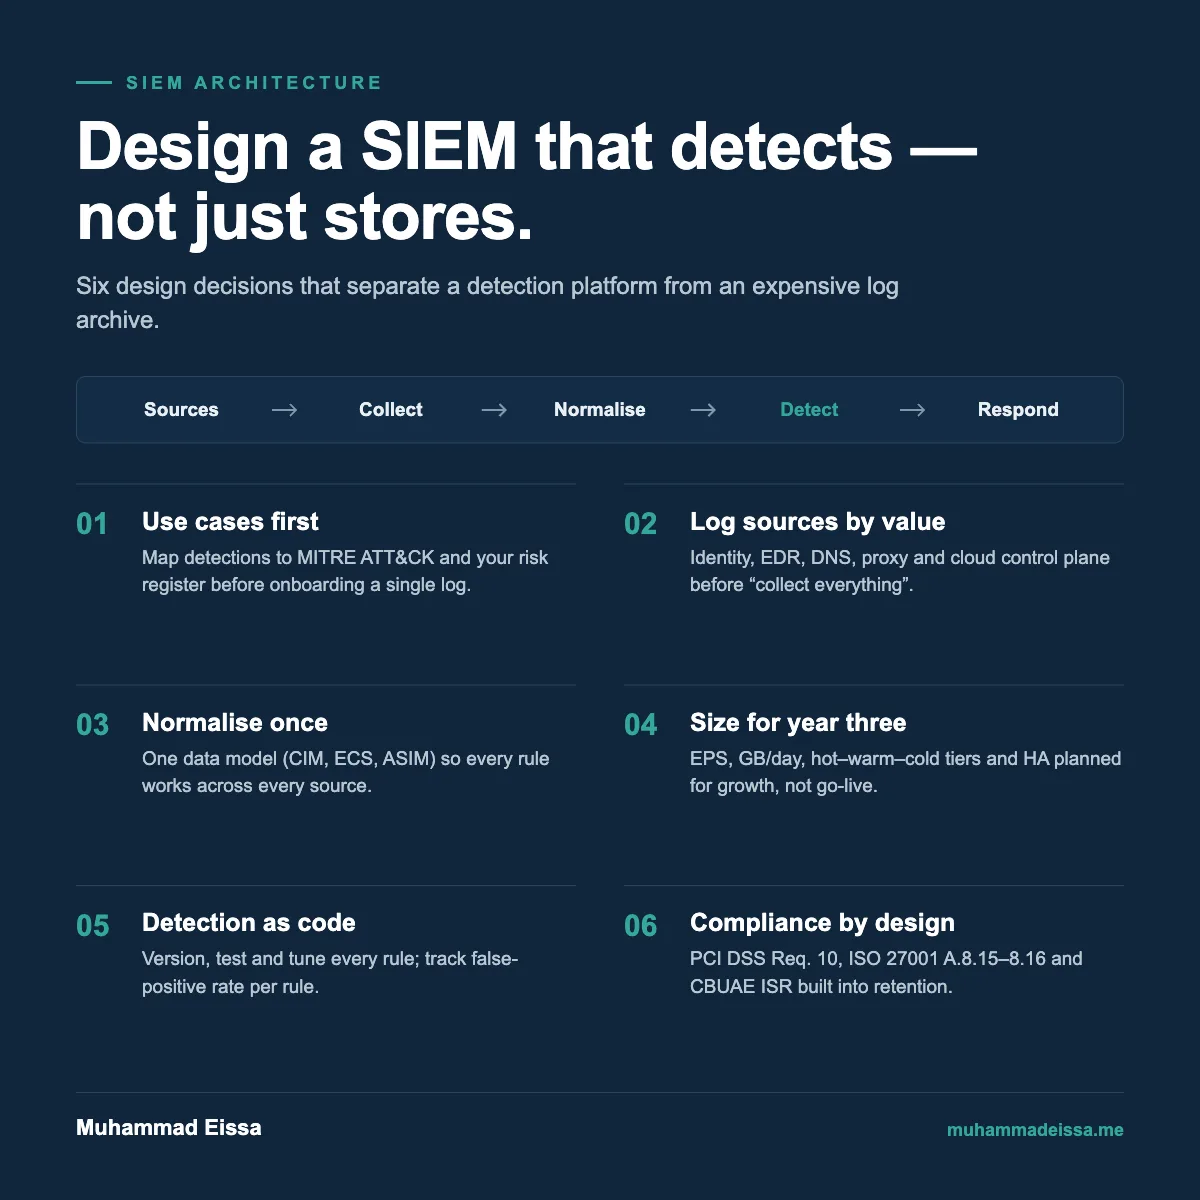
Designing a SIEM that detects, not just stores
Over 13 years across SOC, audit and GRC, I’ve seen the same pattern many times. An organisation buys a top-tier SIEM, onboards every log it can find, and 18 months later has a large licence bill, thousands of untuned alerts, and very few real detections.
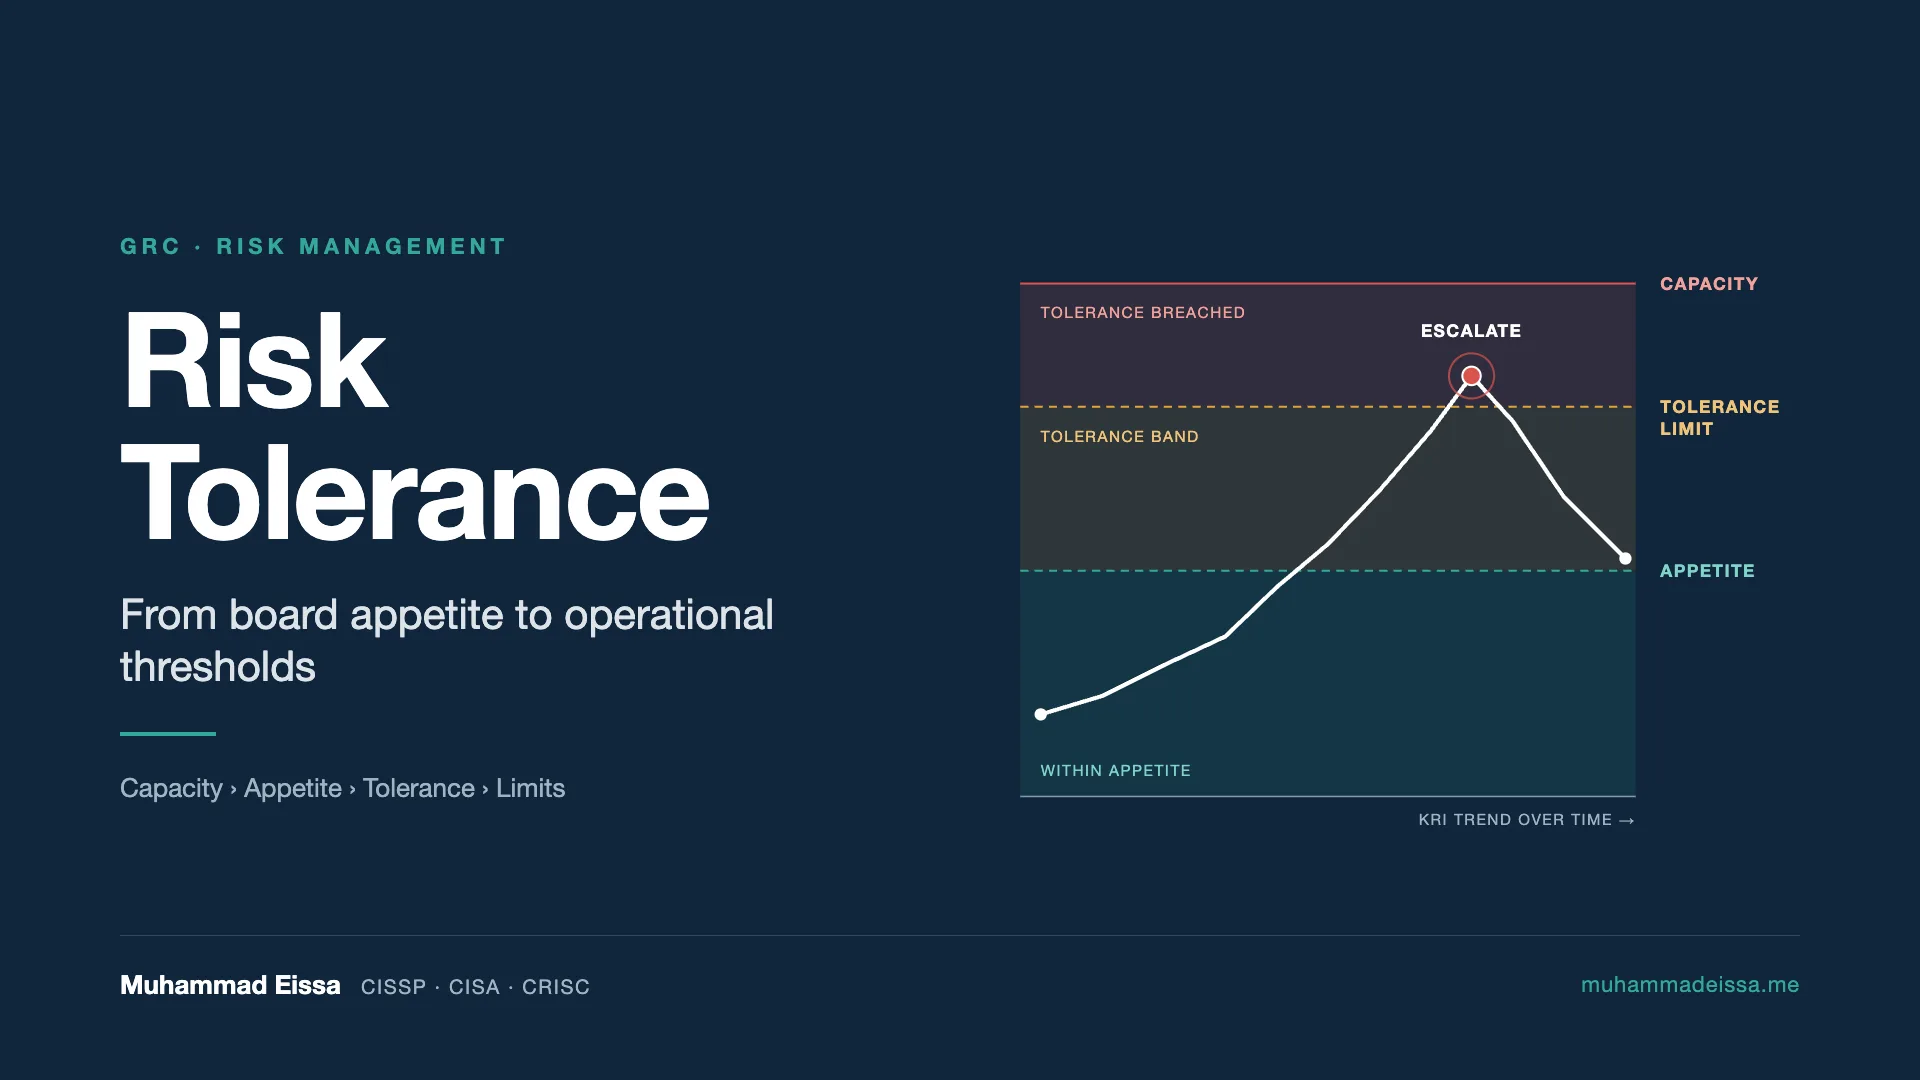
Risk Tolerance: From Board Appetite to Operational Thresholds
Risk tolerance is the measurable boundary that turns a board's risk appetite into a decision rule people can actually operate. Appetite says how much risk the organization is willing to pursue; tolerance says how far actual outcomes may drift before someone must act.
Control assurance through operational evidence
Questions that connect a written security control with evidence of its operation.
From SOC alert to defensible evidence
A practical way to separate observed facts, hypotheses and decisions in a security handoff.
Security response with business context
How to make response recommendations clear about scope, authority and service impact.
Operationalizing the CIA Triad in SOC Operations
Make confidentiality, integrity and availability a practical coverage map for SOC detection, response and assurance.